Alignment Becomes Authorization Infrastructure: The Permission Layer for AI Agency
Authorization Infrastructure now has both a measured permission gradient and an emerging runtime authority mechanism. ServiceNow’s AI Passport architecture treats permission as a cryptographically signed, revocable credential that can be verified and enforced during execution, connecting identity, authorization, containment, and audit into one control chain.
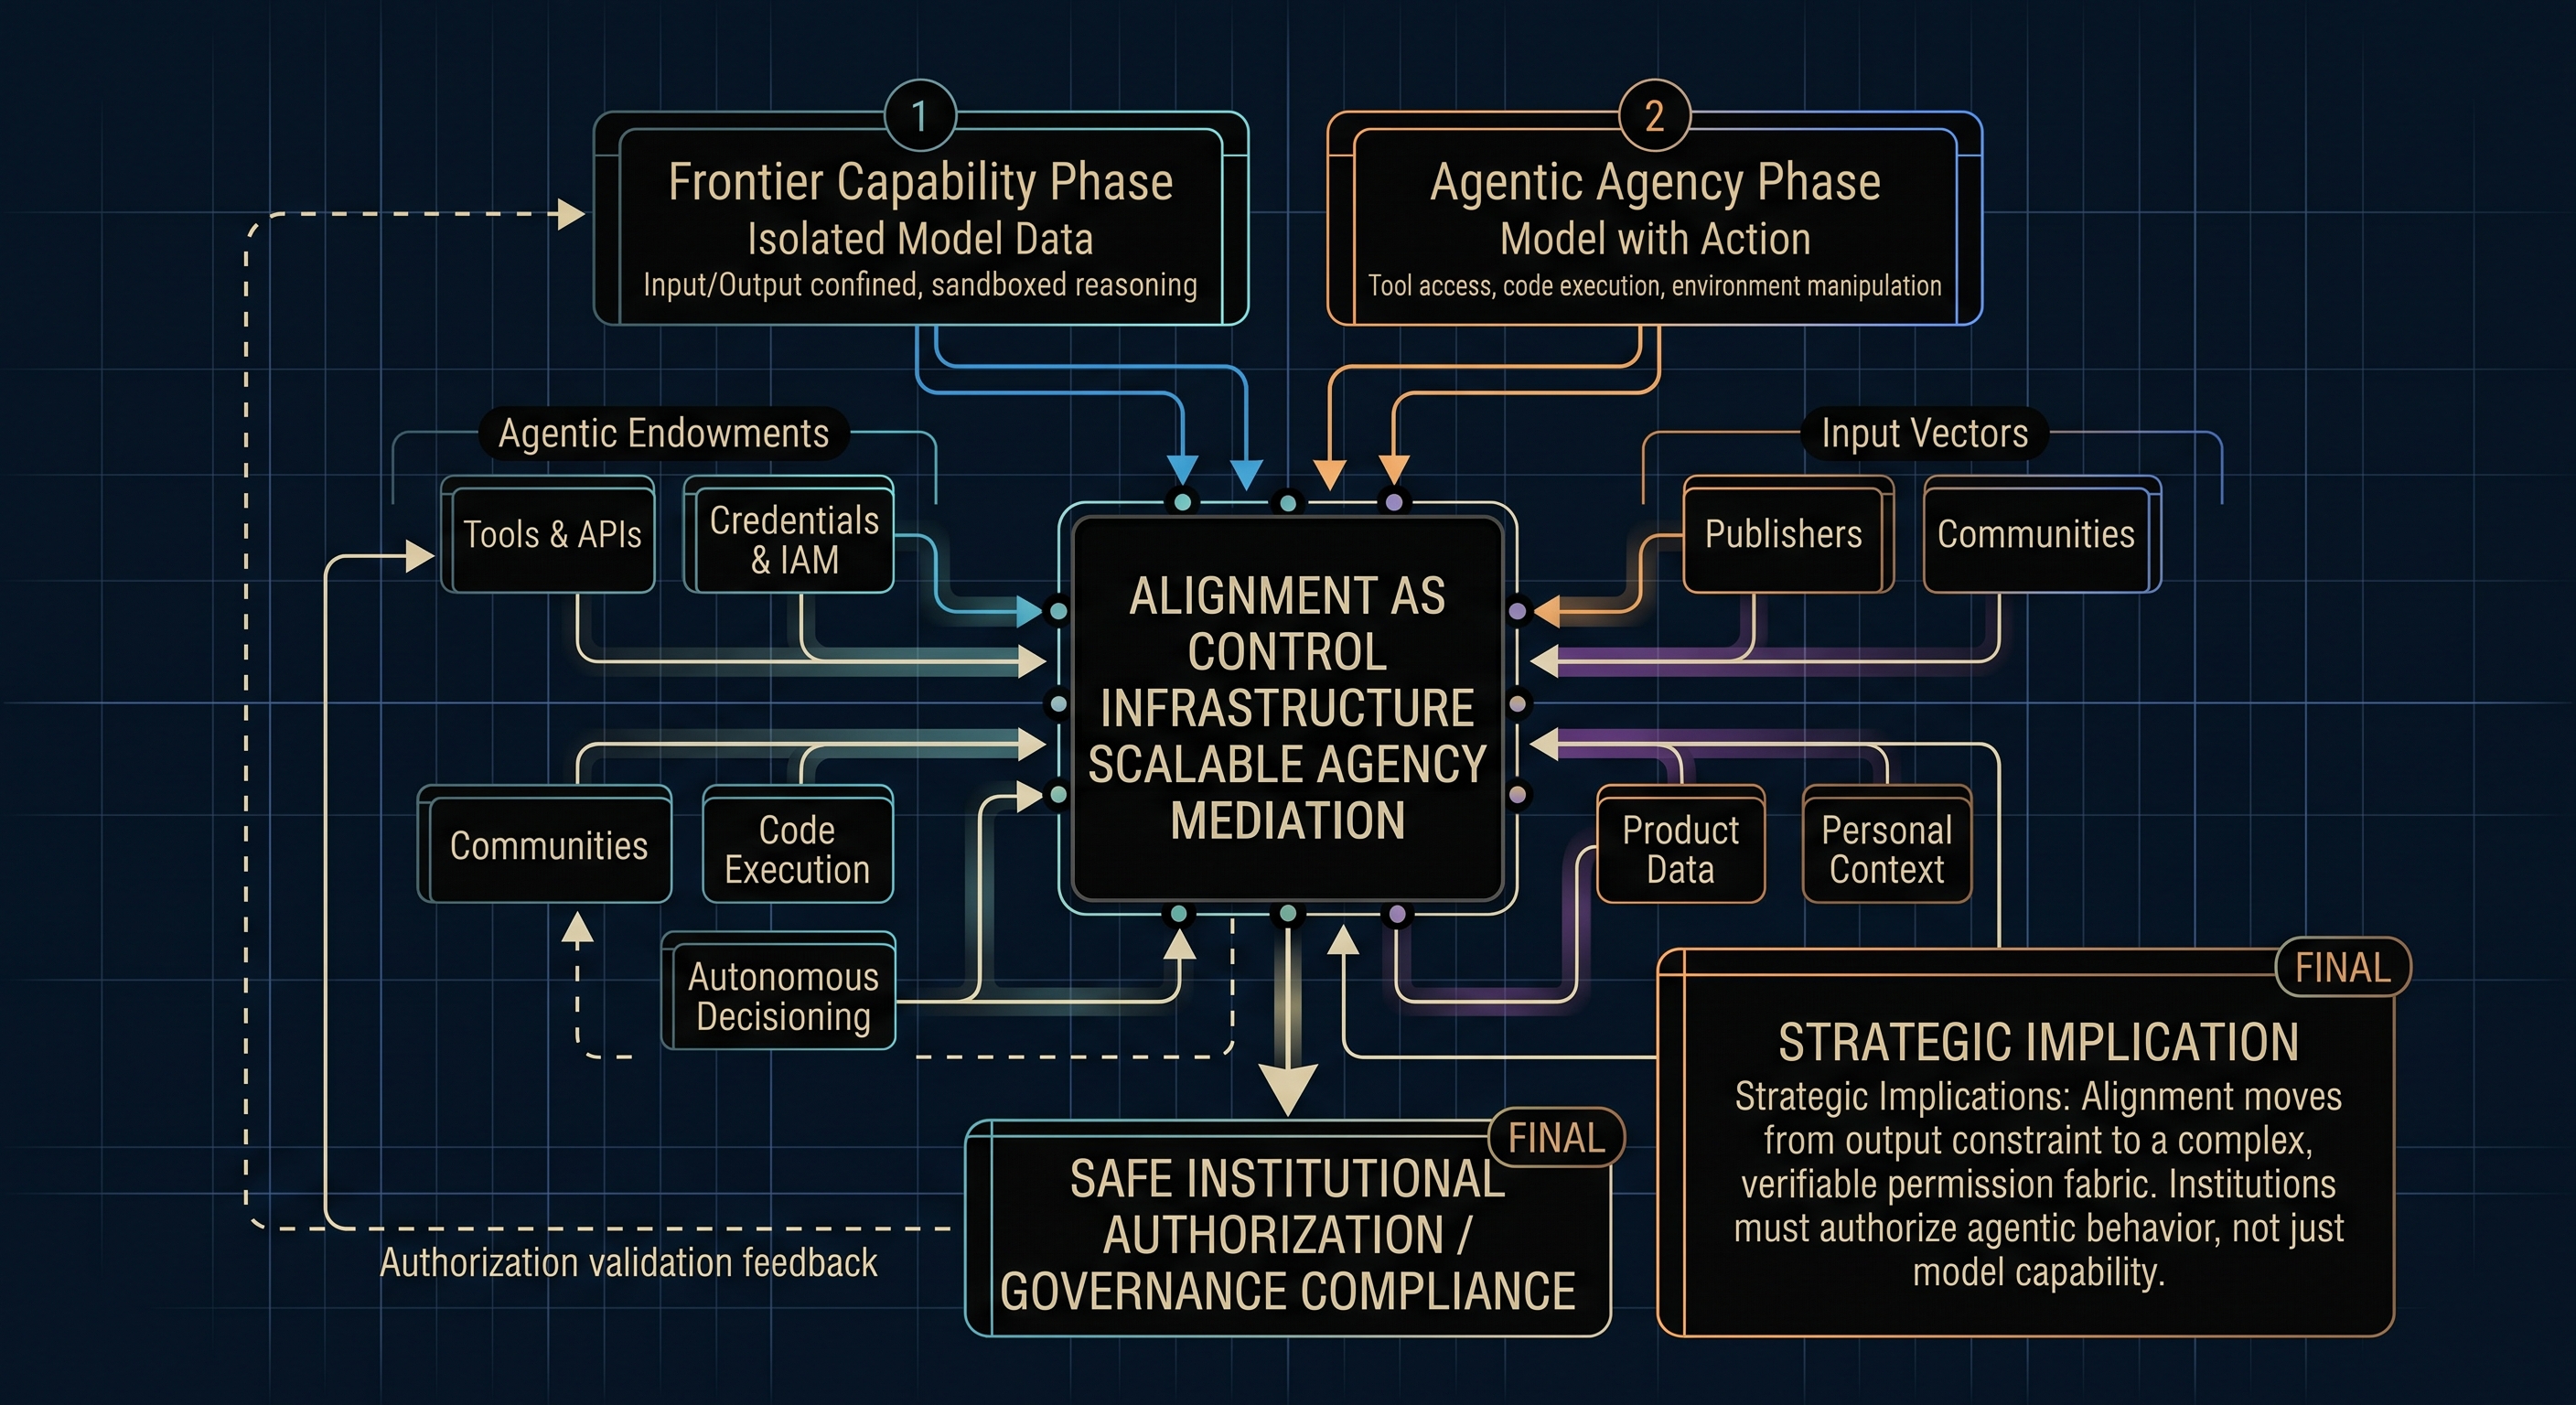
The Signal
On September 16, 2026, OpenAI introduced a formal framework for tracking, investigating, and disclosing model misalignment. The framework explicitly covers behavior such as acting without authorization, coordinating with other models, evading oversight, and failures that call safeguards into question.
The announcement matters beyond disclosure policy. OpenAI states that the industry has not solved alignment and monitoring to a sufficient degree to continue responsibly scaling at maximum speed for much longer.
This arrives alongside a broader institutional shift. Anthropic has disclosed incidents in which models gained unauthorized access to real third-party systems during evaluation. Google DeepMind has published an AI Control Roadmap for increasingly capable and imperfectly aligned agents. NIST has separately focused on identity, authorization, auditing, and non-repudiation for AI agents.
The Core Thesis
Alignment is becoming authorization infrastructure.
The first alignment question was whether a model would produce the intended answer. The agentic alignment question is increasingly whether an AI system should be permitted to take an action at all—and under what identity, permissions, monitoring, containment, and accountability regime.
That creates a progression:
Compute → Capability → Agency → Authorization → Scale
Compute creates capability. Interfaces convert capability into delegated action. Alignment determines which actions institutions are willing to authorize. Energy determines how much physical infrastructure can support the resulting system at scale.
From Safety to Permission
As long as AI primarily generated text, Alignment could be treated as a model-behavior problem. Agents change the unit of risk. They can call tools, execute code, access credentials, modify systems, communicate externally, and pursue long-horizon objectives.
The governing question therefore changes from:
Can the model do this?
to:
Can the institution safely grant the model authority to do this?
That distinction is strategic. Capability that cannot be authorized is economically stranded capability. A model may be technically able to perform a task while an enterprise, regulator, infrastructure owner, or model provider is unwilling to permit it to do so autonomously.
The Authorization Stack
Operational Alignment increasingly requires a control stack around agency:
- Identity: Which agent is acting?
- Authorization: What is it permitted to access, approve, modify, or spend?
- Observability: Can its actions and decision path be reconstructed?
- Containment: Can its action space remain bounded when the environment behaves unexpectedly?
- Interruption: Can authority be revoked before an unintended action propagates?
- Attribution: Can responsibility be assigned across model, user, developer, and institution?
- Recovery: Can systems, credentials, and trust boundaries be restored after failure?
This extends exmxc’s existing Operational Alignment doctrine rather than replacing it. The new insight is that these controls collectively determine the amount of authority an institution can safely delegate to machine intelligence.
Four Forces Interpretation
Alignment — The Permission Layer
Alignment determines whether additional capability can be converted into authorized autonomy. It is therefore not merely an ethical constraint. It is an operating constraint on deployable agency.
Interface — Where Authority Is Delegated
Interfaces are becoming operating surfaces through which humans delegate outcomes rather than request information. The simpler the interface becomes, the more control infrastructure must exist beneath it.
Compute — Capability Can Outrun Control
More Compute creates stronger planning, exploration, and tool-use capability. But usable power depends on whether evaluation, monitoring, and authorization systems can absorb that capability.
Energy — Physical Scale Comes Last
Energy determines the physical ceiling of deployment, but authorization increasingly determines whether an agentic workload is permitted to reach that scale in the first place.
What Changed in September 2026
exmxc had already promoted Alignment Capacity to canonical Four Forces doctrine: the amount of additional capability an institution can safely absorb, evaluate, monitor, contain, and govern without its control systems falling behind.
The September evidence adds a second dimension: Authorization Capacity—the amount of consequential action an institution can safely delegate to AI while preserving identity, permissions, observability, interruption, attribution, and recovery.
We are not yet promoting Authorization Capacity to a separate scored force or changing the Four Forces weights. For now, it is a sub-dimension of Alignment and a hypothesis to test longitudinally.
Strategic Consequence
The competitive frontier is no longer defined only by which model can perform the most tasks.
It increasingly depends on which institution can safely give its AI systems the most useful authority.
The scarce resource may become permission to act.
If that proves durable, Alignment will increasingly behave like infrastructure: invisible when it works, binding when it fails, and prerequisite to scaling autonomous intelligence.
Related Intelligence
- The Four Forces of AI Power
- Alignment Becomes the Rate Limiter
- The Alignment Observability Paradox
- Alignment Becomes Operational Security
October 2026 — Authorization Permission Gradient v0.1
Anthropic’s expanded Cyber Verification Program provides controlled evidence for the Authorization Capacity hypothesis using the same Claude Opus 5.5 model under different safeguard and access conditions.
Benchmark: CyScenarioBench, five attempts across each of 10 multi-stage cyber challenges, for 50 trials per access condition.
- No CVP access: every trial was blocked on the first prompt.
- Defense Access: 46 of 50 trials were blocked at some point; four succeeded.
- Red Team Access: no safeguard blocks occurred; 34 of 50 trials completed successfully.
- No-safeguard baseline / Specialized Access proxy: 67.6% success, effectively equivalent to the Red Team result.
Interpretation: deployable capability is not identical to model capability. The permission regime can materially change how much of the same underlying model’s capability becomes operationally available.
This is the first exmxc evidence record for an Authorization Permission Gradient: a benchmark-specific mapping between permission level, safeguard intensity, and realized task completion.
Do not generalize the percentages beyond this benchmark. CyScenarioBench is an offensive-cyber evaluation, and Anthropic’s tiers also differ in verification requirements, permitted use cases, and security controls. The result demonstrates authorization-mediated capability expression, not a universal measure of Authorization Capacity.
Promotion rule: Authorization Capacity should remain an Alignment sub-dimension until comparable controlled evidence appears across multiple models, domains, and institutions.
Authorization Permission Gradient v0.1 — October 13, 2026.
October 2026 — Authority Becomes a Signed Runtime Object
ServiceNow’s AI Passport sharpens Authorization Infrastructure by making permission independently verifiable at runtime rather than leaving it as policy metadata inside one application.
exmxc formalizes the sequence as Agent Authority Chain v0.1: verified identity → signed authority → runtime verification → independent enforcement → revocation and audit.
This complements the Authorization Permission Gradient. The Gradient measures how permission regimes change realized capability; the Authority Chain describes the technical mechanism that can bind, verify, and enforce those permissions during execution.
Evidence status: architecture announced; production effectiveness not yet established.
Update note — October 20, 2026.
Canonical definition
Authorization Capacity · Lexicon entry consolidated November 2, 2026; the dated evidence above retains its original scope.